
CY0-001 CompTIA SecAI+ v1 Exam Topics and Questions
These CompTIA SecAI+ v1 Exam (CY0-001) exam topics are organized according to official exam domains to help candidates quickly verify coverage and focus on assessment rather than theory. Each domain is paired with topic-wise CY0-001 sample questions that reflect how objectives are tested in the actual exam. This structure enables efficient review, targeted self-assessment, and rapid identification of weak areas when preparing for the CompTIA SecAI+ v1 Exam certification exam.
Let's Practice Free CompTIA CY0-001 Questions Aligned with Official Exam Topics
This topic sets the vocabulary for everything that follows. Before you can defend an AI system or use one as a security tool, you need to know what the underlying mechanisms actually do and where they fail. The exam tests this topic at the concept level, not the code level, but vague answers will cost you. The distinctions between machine learning, deep learning, NLP, and automation matter more than most candidates expect. How Basic AI concepts related to cybersecurity is...
This topic sets the vocabulary for everything that follows. Before you can defend an AI system or use one as a security tool, you need to know what the underlying mechanisms actually do and where they fail. The exam tests this topic at the concept level, not the code level, but vague answers will cost you. The distinctions between machine learning, deep learning, NLP, and automation matter more than most candidates expect.
How Basic AI concepts related to cybersecurity is tested
At 17%, this topic accounts for a meaningful slice of the exam, and the items here tend to be the ones candidates underestimate. The questions do not ask you to train a model or write code. They ask you to classify a described technique, match a threat to its underlying AI mechanism, or identify why a particular AI application fits a particular security use case.
The trap is treating this as pure memorisation. Items reward the ability to distinguish between concepts under pressure: recognising that adversarial machine learning is an attack on the model itself, not just a sophisticated phishing campaign, for instance. Generative AI misuse is a live area, and items in this space tend to describe a scenario and ask you to name the threat category or the defensive implication.
Candidates lose marks by conflating automation with machine learning, or by treating deep learning as simply a synonym for AI. The ranking of specificity matters. Read every scenario carefully before committing to a category.
The ITExamsTopics practice test lets you filter questions by topic, so you can run the concept-heavy items from this domain in isolation and quickly spot which AI categories you are still mixing up, without re-reading a textbook chapter to find out.
The question below puts one of these concept distinctions in a scenario context. Work through it before checking the answer.
Which of the following describes the number of training cycles used in an AI model for threat detection?
With the foundational vocabulary in place, the exam shifts its weight dramatically. At 40%, this is where the exam is won or lost. The topic covers the full lifecycle of keeping an AI system from becoming a liability: controls on the data feeding it, the model itself, and the environment it runs in. Expect scenario-heavy items that force you to choose the right control for a specific threat, not just name a safeguard in the abstract. How Securing AI systems...
With the foundational vocabulary in place, the exam shifts its weight dramatically. At 40%, this is where the exam is won or lost. The topic covers the full lifecycle of keeping an AI system from becoming a liability: controls on the data feeding it, the model itself, and the environment it runs in. Expect scenario-heavy items that force you to choose the right control for a specific threat, not just name a safeguard in the abstract.
How Securing AI systems is tested
Forty percent of the exam lives here, so the item count is substantial and the scenarios are detailed. Items present a described AI deployment and ask which control addresses a stated risk, or they describe a gap in a data pipeline and ask what the attacker can now do. Both directions appear.
The adversarial risk sub-area is particularly active. Items reward candidates who can identify the attack surface being targeted: the training data, the model weights, or the inference endpoint. These are not interchangeable, and items are written to separate candidates who know the difference from those who guess.
Deployment environment matters too. A control that is appropriate on-premises may not translate cleanly to a cloud or hybrid setup, and items are constructed to surface that gap. Candidates lose marks by applying generic security advice without anchoring it to the AI-specific context in the scenario. Read the environment details before selecting a control. The strongest option addresses both the AI-specific threat and the deployment context simultaneously.
Because this topic represents 40% of the exam, you need volume. Working through a full question bank under timed conditions reveals which control categories you apply confidently and which ones slow you down when the scenario adds a deployment-environment wrinkle.
The question below places you in a scenario where a specific AI asset is under threat. Decide on your control before reading the options.
An architect is using the firm's recommended large language model (LLM) to find an internal solution for content management.
Given the following:
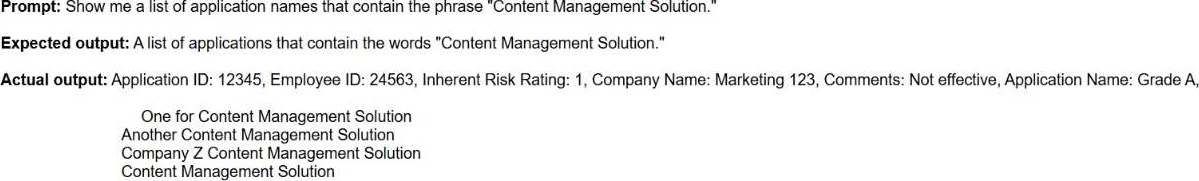
Which of the following controls is the best for mitigating this issue?
Securing AI is one direction; using AI as a security tool is the other. This topic covers the operational side: how AI-driven detection, automated triage, and continuous monitoring change the way security teams work, and what candidates must know to apply those tools correctly. The gap between topic 2 and this one is the direction of the problem. Here the AI is on your side, and the exam asks whether you are using it effectively. How AI-assisted security is tested...
Securing AI is one direction; using AI as a security tool is the other. This topic covers the operational side: how AI-driven detection, automated triage, and continuous monitoring change the way security teams work, and what candidates must know to apply those tools correctly. The gap between topic 2 and this one is the direction of the problem. Here the AI is on your side, and the exam asks whether you are using it effectively.
How AI-assisted security is tested
At 24%, this topic generates a significant number of items, and they skew operational. Scenarios describe a SOC environment, a detection pipeline, or a threat-modeling exercise and ask you to identify where AI adds value, or where a team is misapplying it.
Items on detection and response reward candidates who understand the difference between anomaly detection flagging an event and a human analyst confirming a true positive. AI accelerates triage; it does not eliminate judgment. Questions are written to catch candidates who treat AI output as final.
The workflow automation sub-area tests alert correlation and response orchestration specifically. Items here describe a sequence of events and ask which step AI should handle and which step requires human decision-making. Getting that boundary wrong is the most common way to lose marks in this topic.
Behavior analysis and continuous monitoring items often hinge on what the AI is trained to baseline. Candidates who treat monitoring as a passive activity rather than a tuned, ongoing process tend to select options that sound reasonable but miss the AI-specific operational requirement.
A free demo of the ITExamsTopics practice test lets you sample the item style for this topic before committing, so you can judge whether your operational AI knowledge holds up under exam conditions rather than discovering the gap on the day.
The question below describes an operational scenario where an AI tool is in the loop. Pin down the boundary of AI responsibility before answering.
The final topic pulls back from the technical layer and asks what rules govern AI in the first place. Regulatory frameworks, ethical obligations, and lifecycle-level GRC practices all appear here. If your background is purely technical, this is the area most likely to have gaps. The exam does not reward knowing that GDPR exists; it rewards knowing what GDPR and the NIST AI RMF require of the people building and operating AI systems. How AI governance, risk, and compliance is...
The final topic pulls back from the technical layer and asks what rules govern AI in the first place. Regulatory frameworks, ethical obligations, and lifecycle-level GRC practices all appear here. If your background is purely technical, this is the area most likely to have gaps. The exam does not reward knowing that GDPR exists; it rewards knowing what GDPR and the NIST AI RMF require of the people building and operating AI systems.
How AI governance, risk, and compliance is tested
At 19%, this topic is not a minor appendix to the exam. Items here are often scenario-based: a company is deploying an AI system in a regulated industry, and you must identify which governance requirement applies, which lifecycle stage it applies to, or which ethical principle the described practice violates.
The regulatory framework sub-area tests global scope. Items may describe a data-handling practice and ask which jurisdiction's rules it breaches, or describe a risk management gap and ask which framework element addresses it. Candidates who know only one framework by name tend to guess on these.
The GRC integration sub-area rewards candidates who understand that governance is not a checkpoint at deployment but a practice woven through the full AI lifecycle, from data sourcing to model retirement. Items are written to surface candidates who treat compliance as a one-time sign-off.
Ethical guidelines items often present a tension between business utility and individual rights. The strongest option in those items reflects the framework's stated priority order, not general common sense. Knowing the hierarchy inside NIST AI RMF and the principles behind GDPR is what separates a confident answer from a coin flip.
Use the ITExamsTopics PDF alongside the practice test to cross-check your governance coverage topic by topic. Seeing exactly which framework-specific items you miss is faster than re-reading the regulation itself to find where your knowledge stops.
The question below puts a real-world governance tension in front of you. Identify the applicable framework requirement before looking at the options.
Ready to Start Practicing?
Access all questions and start your exam preparation journey
Upgrade to Full CY0-001 Exam Questions 🚀


