1. Home
  2. Cisco
  3. 350-201 Exam

350-201 Performing Cybersecurity Using Cisco Security Technologies Exam Topics and Questions

Let's Practice Free Cisco 350-201 Questions Aligned with Official Exam Topics

Follows Cisco's official outline Updated 08 Sep, 2026 4 Topics
Reviewed by Thomas Lee, Cisco 350-201 Certified Professional
Topic Content
1.0 Fundamentals Interpret the components and structure of security playbooks to understand their purpose and application in incident response scenarios. Determine the appropriate tools and technologies required based on specific playbook requirements and organizational needs. Apply established playbooks to common security incidents including unauthorized privilege escalation, Denial of Service DoS and Distributed Denial of Service DDoS attacks, and website defacement incidents. Identify relevant compliance standards and their corresponding industries, including PCI DSS, FISMA, FedRAMP, SOC 2, SOX, GDPR, Data Privacy regulations,... See More
Sample Questions for Topic 1 : 1.0 Fundamentals
Q1

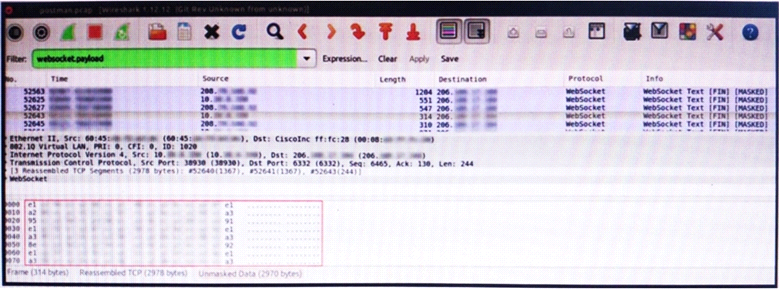
Refer to the exhibit.

An engineer is analyzing this Vlan0386-int12-117.pcap file in Wireshark after detecting a suspicious network activity. The origin header for the direct IP connections in the packets was initiated by a google chrome extension on a WebSocket protocol. The engineer checked message payloads to determine what information was being sent off-site but the payloads are obfuscated and unreadable. What does this STIX indicate?

Topic Content
2.0 Techniques encompasses a comprehensive range of security practices and methodologies. This includes selecting appropriate data analytics techniques for specific business questions, implementing hardened machine images for secure deployment, and conducting thorough security posture assessments of organizational assets. Professionals must evaluate existing security controls, identify gaps, and recommend improvements while determining resources for industry standards and system hardening guidelines. The section covers practical implementation skills such as recommending patching strategies, disabling unnecessary services, applying network segmentation, and utilizing network controls... See More
Sample Questions for Topic 2 : 2.0 Techniques
Q2

An engineer is investigating several cases of increased incoming spam emails and suspicious emails from the HR and service departments. While checking the event sources, the website monitoring tool showed several web scraping alerts overnight. Which type of compromise is indicated?

Topic Content
3.0 Processes encompasses the systematic methodologies and procedures required for effective cybersecurity incident investigation and response. This includes prioritizing components within threat models to focus resources on critical assets, and determining appropriate investigation steps for common security cases. The malware analysis process is a core competency, requiring the ability to extract and identify samples from various sources such as packet captures, perform reverse engineering techniques, conduct dynamic analysis in sandbox environments, and execute static analysis when needed. Professionals must interpret... See More
Topic Content
4.0 Automation and Orchestration encompasses the fundamental skills required to automate security operations and infrastructure management. Candidates must compare different orchestration platforms and automation mechanisms to understand their respective advantages and use cases. This domain requires proficiency in interpreting and modifying basic scripts, particularly Python, to automate security tasks and operations. Understanding common data formats such as JSON, HTML, CSV, and XML is essential for working with APIs and data interchange. Candidates should be able to identify opportunities for automation... See More

Ready to Start Practicing?

Access all questions and start your exam preparation journey

Upgrade to Full 350-201 Exam Questions 🚀
Exams Made Simple. Success Made Possible.